- by foxnews
- 13 Oct 2026
Why verified social media accounts can still lead you into a scam
Microsoft's X account was hijacked to promote a crypto pump-and-dump scheme, exposing its more than 13 million followers to a scam campaign.
- by foxnews
- 13 Oct 2026
- in technology
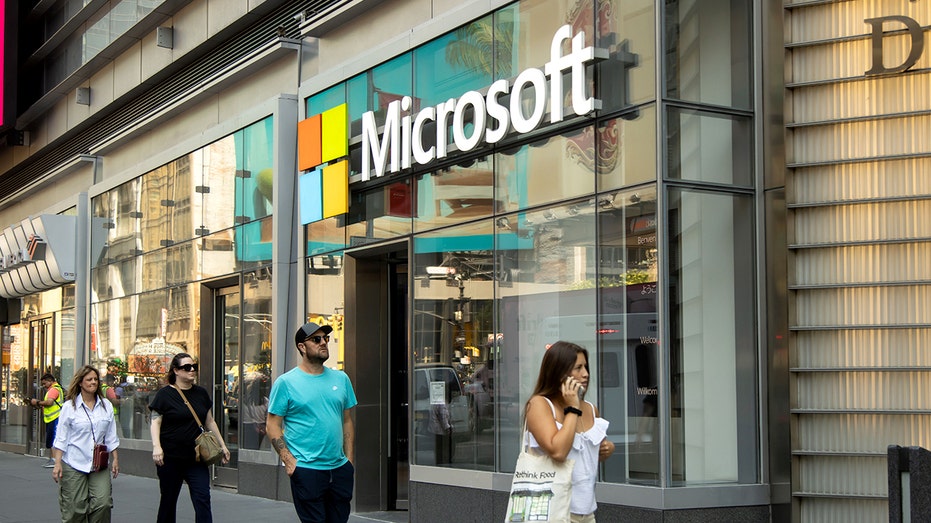
We have all developed little shortcuts for deciding whether something online looks legitimate. You check the account name. You recognize the company logo. Then you spot that verification badge and your guard comes down a little. That can be exactly what scammers are counting on.
Microsoft's official X account became the latest reminder after attackers gained unauthorized access and used the account in an apparent cryptocurrency pump-and-dump scheme. The account has more than 13 million followers, giving whoever controlled it access to a huge audience and the credibility that comes with Microsoft's name.
Here is what happened, why compromised verified accounts can be so convincing and what you should check before trusting the next surprising post that shows up in your feed.
Join us for a free CyberGuy LIVE class.
Kurt "CyberGuy" Knutsson shares practical ways to stay safer, smarter and more confident with technology. Explore classes on stopping spam, phone security, financial protection and using AI to get better health care . Each class is free, easy to follow and comes with a free printable checklist .
See the classes and register at CyberGuyLive.com
BleepingComputer reported that Microsoft's @Microsoft account followed and reposted content from another X account that appeared to be Clippy-themed. That account was promoting a cryptocurrency called $Clippy. Microsoft tells CyberGuy that two unauthorized posts appeared during the period when its account was compromised. According to the company, the first was a quote repost of content from what appeared to be a Clippy-themed account and referenced bringing back Microsoft Office's old animated paperclip character. The second appeared to be an apology related to the earlier activity. Microsoft says neither post originated from the company.
A Microsoft spokesperson provided CyberGuy with the following statement: "We have confirmed unauthorized access to our account on X, including posts that did not originate from Microsoft. The account has been secured, the unauthorized posts have been removed, and we are continuing to investigate the circumstances."
If an account you have never heard of suddenly tells you Microsoft launched a Clippy cryptocurrency, you might keep scrolling. When Microsoft's actual account appears to amplify that same message, it becomes much easier to hesitate. You may assume someone at the company approved the post. You might click a link because you recognize the account. Someone interested in crypto could move even faster because they are worried about missing an opportunity.
This is also not Microsoft's first encounter with a crypto scam involving one of its X accounts. In June 2024, scammers hijacked Microsoft India's X account and used it to impersonate Keith Gill, better known online as Roaring Kitty. The attackers then promoted what appeared to be a GameStop cryptocurrency presale.
People who followed the link and connected their cryptocurrency wallets risked having their assets stolen through wallet-draining malware. That example shows how quickly a social media takeover can turn into something much more expensive. A post may only be the beginning. The real danger often waits behind the link.
One of the clearest examples happened in January 2024 when attackers took over the U.S. Securities and Exchange Commission's official X account. The compromised account falsely announced that the SEC had approved spot Bitcoin exchange-traded funds. According to the Justice Department, Bitcoin jumped by more than $1,000 following the false post. After the SEC regained control and corrected the announcement, Bitcoin fell by more than $2,000.
A verification badge can still be useful. It may help confirm that an account belongs to the person, company or organization it claims to represent. What it cannot tell you is whether that same organization still controls the account at the exact moment you are reading a post.
You do not need to assume every surprising post is the work of a hacker. Still, when an account suddenly asks you to spend money or connect something valuable, a few extra checks can save you from a painful mistake.
If a company announces a cryptocurrency, giveaway or major investment opportunity on social media, go directly to the company's website. Look for the same announcement in its newsroom or another official channel. If the only place you can find it is one social media post, wait before acting.
If an account that normally talks about software suddenly starts pushing an obscure crypto token, treat that change as a warning sign. Scroll through its recent posts and check whether the promotion fits anything the company has announced elsewhere.
Connecting a cryptocurrency wallet can expose you to malicious approvals that allow attackers to move assets. Navigate directly to a service you already trust instead. Never enter your recovery phrase or private key into a site because a social media post tells you to.
Scammers love deadlines. You may be told a token is launching right now or that an offer disappears in a few minutes. That pressure is designed to get you moving before you verify what you are seeing. Give yourself time to check another source.
Even when the post comes from a legitimate account, the link inside it may lead somewhere dangerous. Look carefully at the web address before entering a password, payment information or crypto credentials. Small changes in a domain name can lead you to an entirely different site.
What you should do next depends on how far you got before realizing something looked suspicious.
The Microsoft attack is a good reminder of how quickly the signals we rely on can turn against us. We tell people to check the account name, look for the real profile and be cautious with impersonators. In this case, attackers briefly had control of the account people were supposed to trust. I would still use verification as one clue, but I would never let a checkmark do the thinking for me when money, passwords or a crypto wallet are involved. If a company suddenly posts something that feels out of character, verify it somewhere else before you act. Go to the company's website, check another official channel and give yourself a minute before clicking. That extra pause can be the difference between spotting a scam and paying for one.
Would you still trust a financial announcement because it came directly from a verified company account, or do attacks like this make the checkmark almost meaningless to you? Let us know by writing to us at Cyberguy.com
Sign up for my FREE CyberGuy Newsletter
Copyright 2026 CyberGuy.com. All rights reserved.
you may also like
- by foxnews
- 13 Oct 2026
The hotel TV privacy mistake that can follow you home
- by foxnews
- 13 Oct 2026
AI voice scam traps mom in 5-hour kidnapping nightmare
travel
- by foxnews
- descember 09, 2016
Woman's routine Uber ride takes alarming turn after her driver misses the exit
A viral TikTok video describes an Uber passenger's 3 a.m. ride turning alarming when her driver asked to stop at a parking garage to charge his EV. Experts weigh in.
read more